Martyn's Law & Event Security: What Venues & Organisers Need To Do
Cronos Protection · 21 August 2026
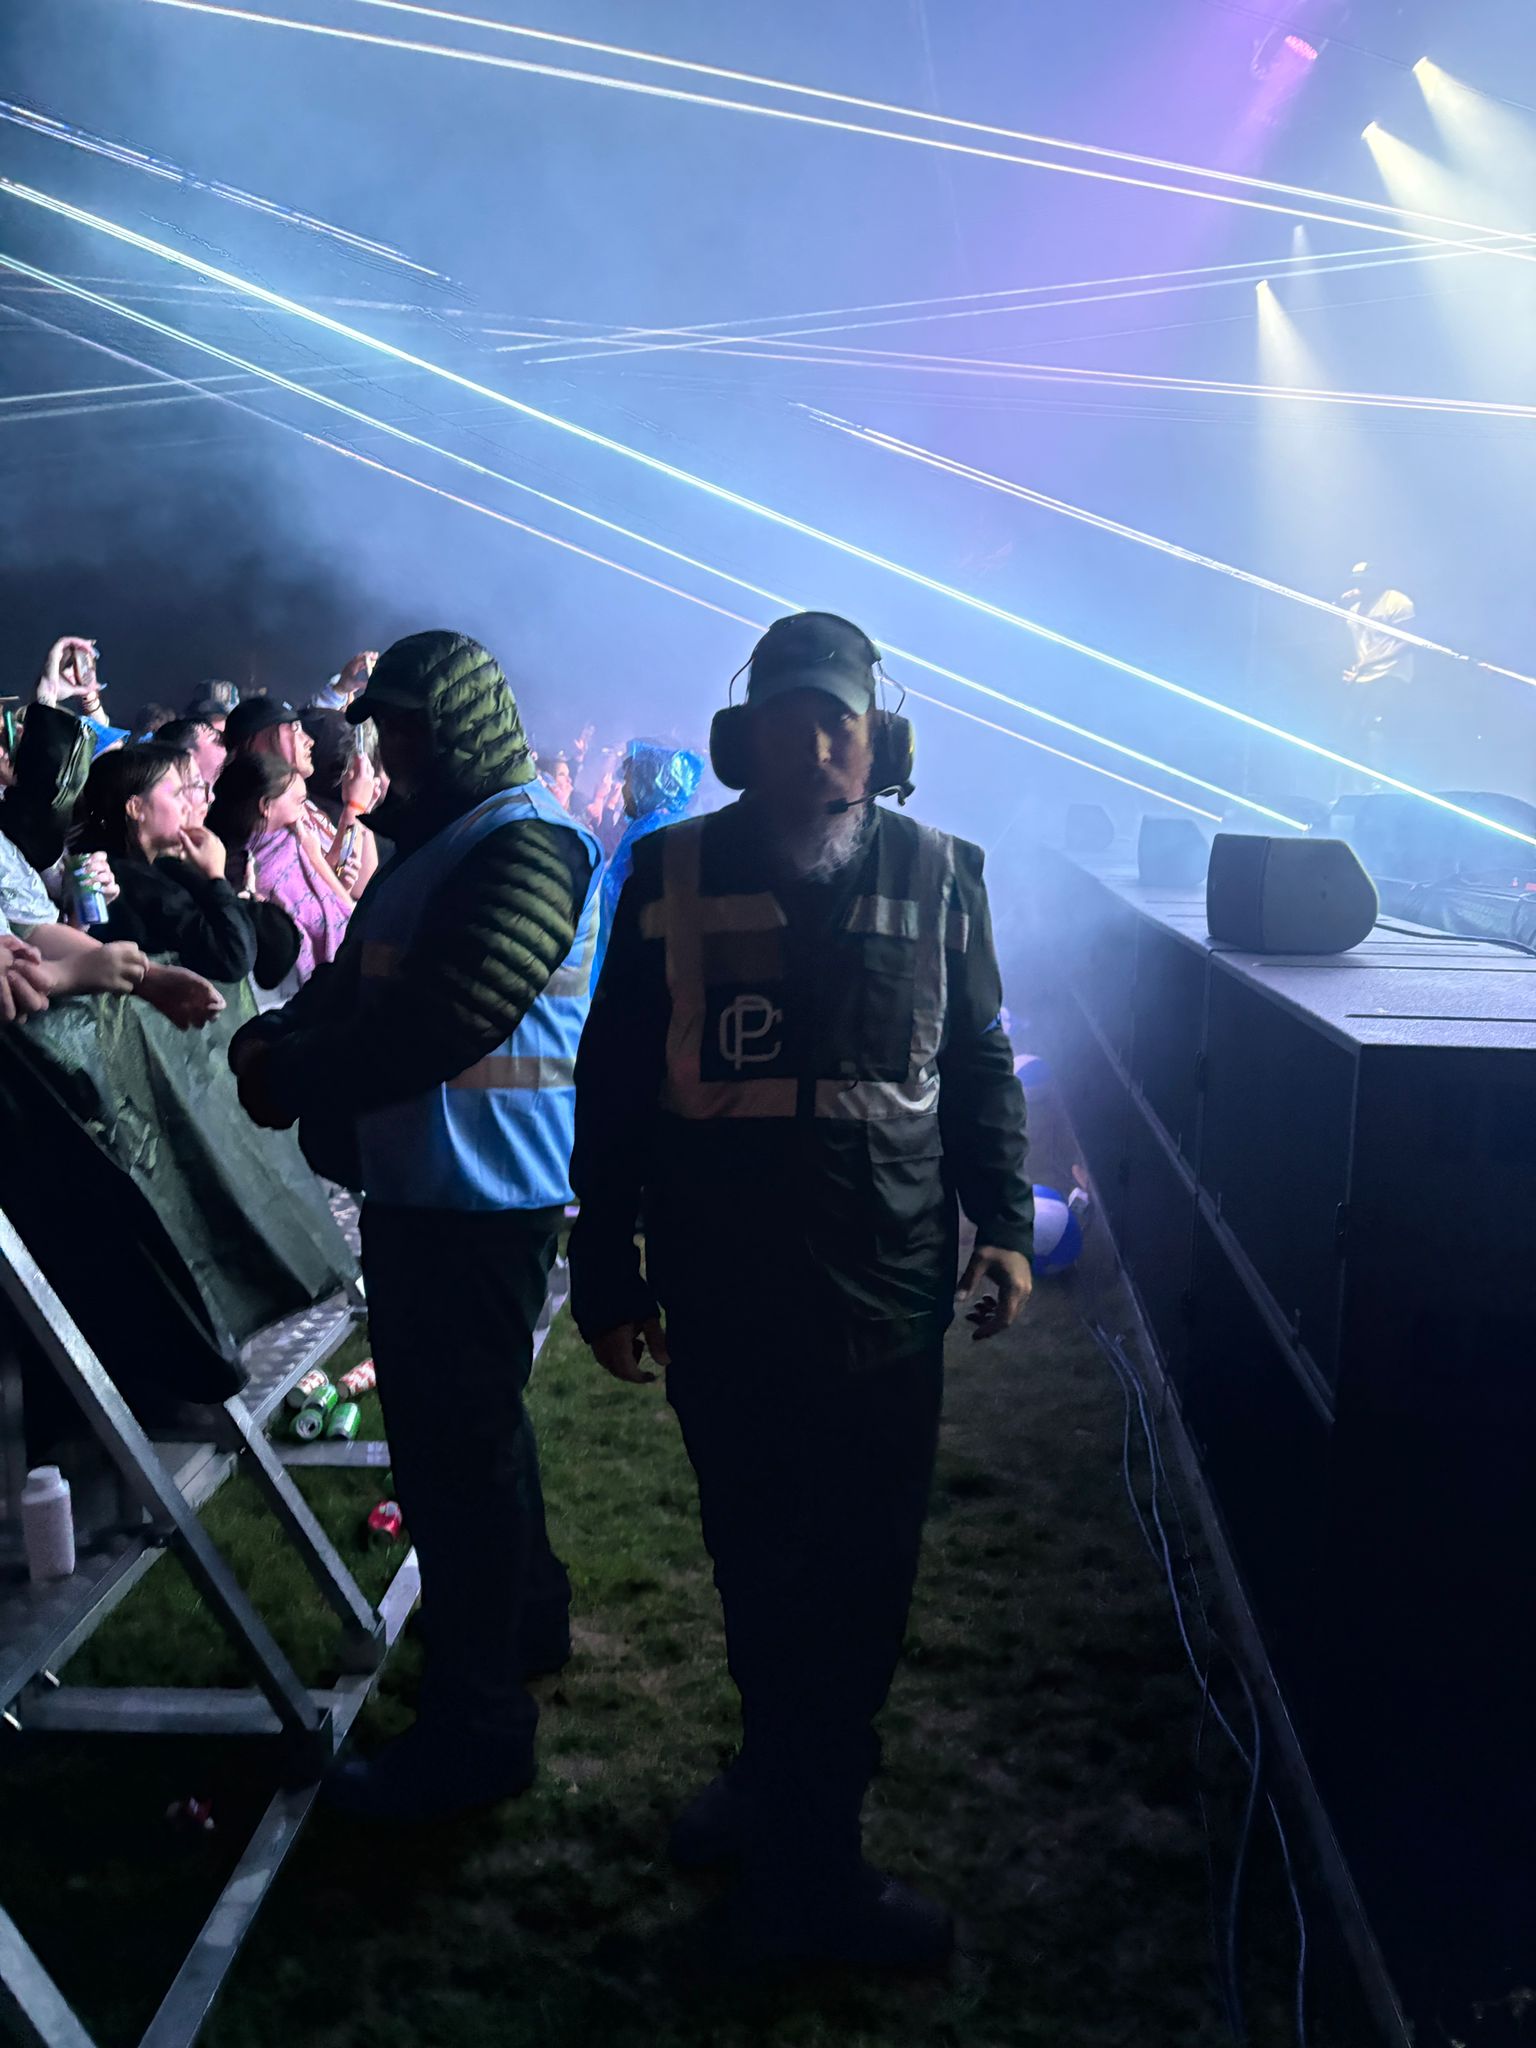
Martyn''s Law is the biggest change to UK venue and event security in a generation, and it turns something most organisers already do informally into a legal duty with a regulator attached.
The Terrorism (Protection of Premises) Act 2025 received Royal Assent in April 2025, named in memory of Martyn Hett, one of the twenty-two people killed in the Manchester Arena attack in 2017. Government has confirmed an implementation period before the duties bite — roughly two years — with the Security Industry Authority acting as regulator.
That period is the window to get ready. Below is what the duties involve and what a compliant operation looks like in practice.
Who the law applies to
The Act applies to qualifying premises and qualifying events where people can reasonably be expected to be present in certain numbers, split into two tiers.
Standard tier: 200 to 799 people
Premises where 200 or more individuals may reasonably be expected to be present. The requirements are proportionate and largely procedural:
Notify the regulator that the premises are in scope.
Have in place public protection procedures — what your people will do in the event of an attack.
Cover evacuation, invacuation (moving people to safety inside), lockdown and communication.
Make sure staff know those procedures, through appropriate instruction.
Standard tier is not intended to require physical works or expensive equipment. It requires a plan, and people who know it.
Enhanced tier: 800 or more people
Larger premises and qualifying events carry the standard-tier duties plus more:
Public protection measures as well as procedures — steps that reduce vulnerability and the risk of physical harm.
A documented assessment of the measures in place.
A designated senior individual responsible for compliance.
Documentation provided to the regulator.
Measures at this tier typically cover monitoring of the premises and surrounding area, movement of people into, out of and within the site, physical safety and security of the premises, and security of information that could assist an attacker.
Procedures versus measures — and why the distinction matters
Procedures are about response: if something happens, what do we do, who says it, where do people go, how do we tell them. Measures are about reducing likelihood and harm before anything happens: how people are screened and directed, how queues are positioned, what is monitored, what an attacker could learn about your site in advance.
Standard tier needs the first. Enhanced tier needs both.
What good looks like on the ground
Counter-terrorism awareness for every person on the team
Attack planning generates observable behaviour: hostile reconnaissance, unusual questions, filming of entrances and control points, testing of access. The people most likely to see it are stewards, box office, cleaners and bar staff — not the security manager.
ACT (Action Counters Terrorism) awareness training is free, short and available to all staff. Every venue in scope should be able to say what proportion of its team has completed it, and should be running SCaN or equivalent behavioural-detection briefings for front-of-house roles. There should also be a simple, well-known internal route for reporting a concern that does not require someone to be certain before they speak up.
Crowd flow and queue management
Queues are frequently the most exposed part of an event, because they concentrate people outside the secured line. Planning should address queue location and depth, whether crowds build against a road or a hard structure, how quickly a queue can be dispersed or held, and how entry throughput is maintained so the queue does not grow.
Egress deserves as much thought as ingress. Most planning effort goes into getting people in; the crush risk and the exit-route problem usually sit at the end of the night.
Search and screening plans
A search regime needs to be written down before the event: what is searched, at what rate, by whom, with what authority, how bag policy is communicated in advance, how refusals and prohibited items are handled, where a secondary search takes place and how records are kept. Percentage searching is legitimate where it is genuinely randomised and enforced — and worthless where it becomes whoever looks convenient.
Communicating a clear bag policy at ticket purchase does more for throughput than any amount of extra staff on the gate.
Stewarding numbers and competence
There is no single legal ratio, and any supplier who quotes one without asking about your event should be treated with caution. Numbers follow the event: audience profile, whether it is seated or standing, alcohol, the number of entry points, the length of the perimeter, egress routes, transport links and the licensing authority''s expectations.
What matters as much as headcount is role clarity — who is on entry search, who holds pit positions, who is on fixed points, who is roving, who is on exit and who is spare for redeployment. A crowd-safety plan that names positions is a plan. A headcount is not.
Medical, welfare and fire
Event safety is not only counter-terrorism. Medical provision, welfare for vulnerable attendees, lost children procedures, fire safety, adverse weather and show-stop procedures all belong in the same document set, with one clear command structure and a single channel that can stop the show.
Documentation the regulator will expect
Whichever tier you are in, keep a live and dated set of:
Notification to the regulator, with the responsible person identified.
Public protection procedures — evacuation, invacuation, lockdown, communication.
For enhanced tier, the assessment of measures in place and their rationale.
Training records showing who completed what, and when.
Search and screening plan, plus bag policy as published to attendees.
Staffing plan by position and shift, with the supplier''s licence details.
Exercise and test records — a walkthrough or tabletop with dates and attendees.
Incident log and post-event debriefs, including what was changed as a result.
The compliance test is straightforward in principle: can you show a plan, show that your people know it, and show that you review it? Undated documents that nobody has read are the most common failing.
Practical steps to take now
Establish your tier by working out the maximum number of people reasonably expected on site.
Name the responsible senior individual, in writing.
Write or refresh your public protection procedures — evacuation, invacuation, lockdown, communication.
Get ACT awareness training completed across the whole team and record it.
Run a tabletop exercise against a realistic scenario and minute what it exposed.
Review your search and bag policy, and publish it with tickets.
Check your security supplier's accreditation, screening standard and counter-terrorism training — see COP 119 explained.
Diarise a review date. A plan written once and never revisited will not stand up.
Where a security provider fits
Most venues and organisers do not need a compliance consultant so much as a supplier that already works this way: trained, screened officers and stewards, written assignment instructions, documented briefings and a debrief that produces changes rather than paperwork.
Cronos Protection provides event security and stewarding and SIA door supervision across Surrey, Kent, Essex, London and the South East, for venues, festivals, corporate events and licensed premises.
If you would like a review of your current stewarding plan and documentation against Martyn''s Law, get in touch.
This article is general guidance, not legal advice. Duties depend on your specific premises or event, and you should refer to the Terrorism (Protection of Premises) Act 2025 and the regulator's published guidance.